“The first sweep found a global admin who had left the company seven months earlier. That one finding paid for the year.”
SOC 2 Type II · ISO 27001 · 1,400 security teams
SOC 2 Type II · ISO 27001 · 1,400 security teams
Palisade
Palisade
Risk score82/100open
Next page/
Home
Case 04 · Fintech · 210 seats
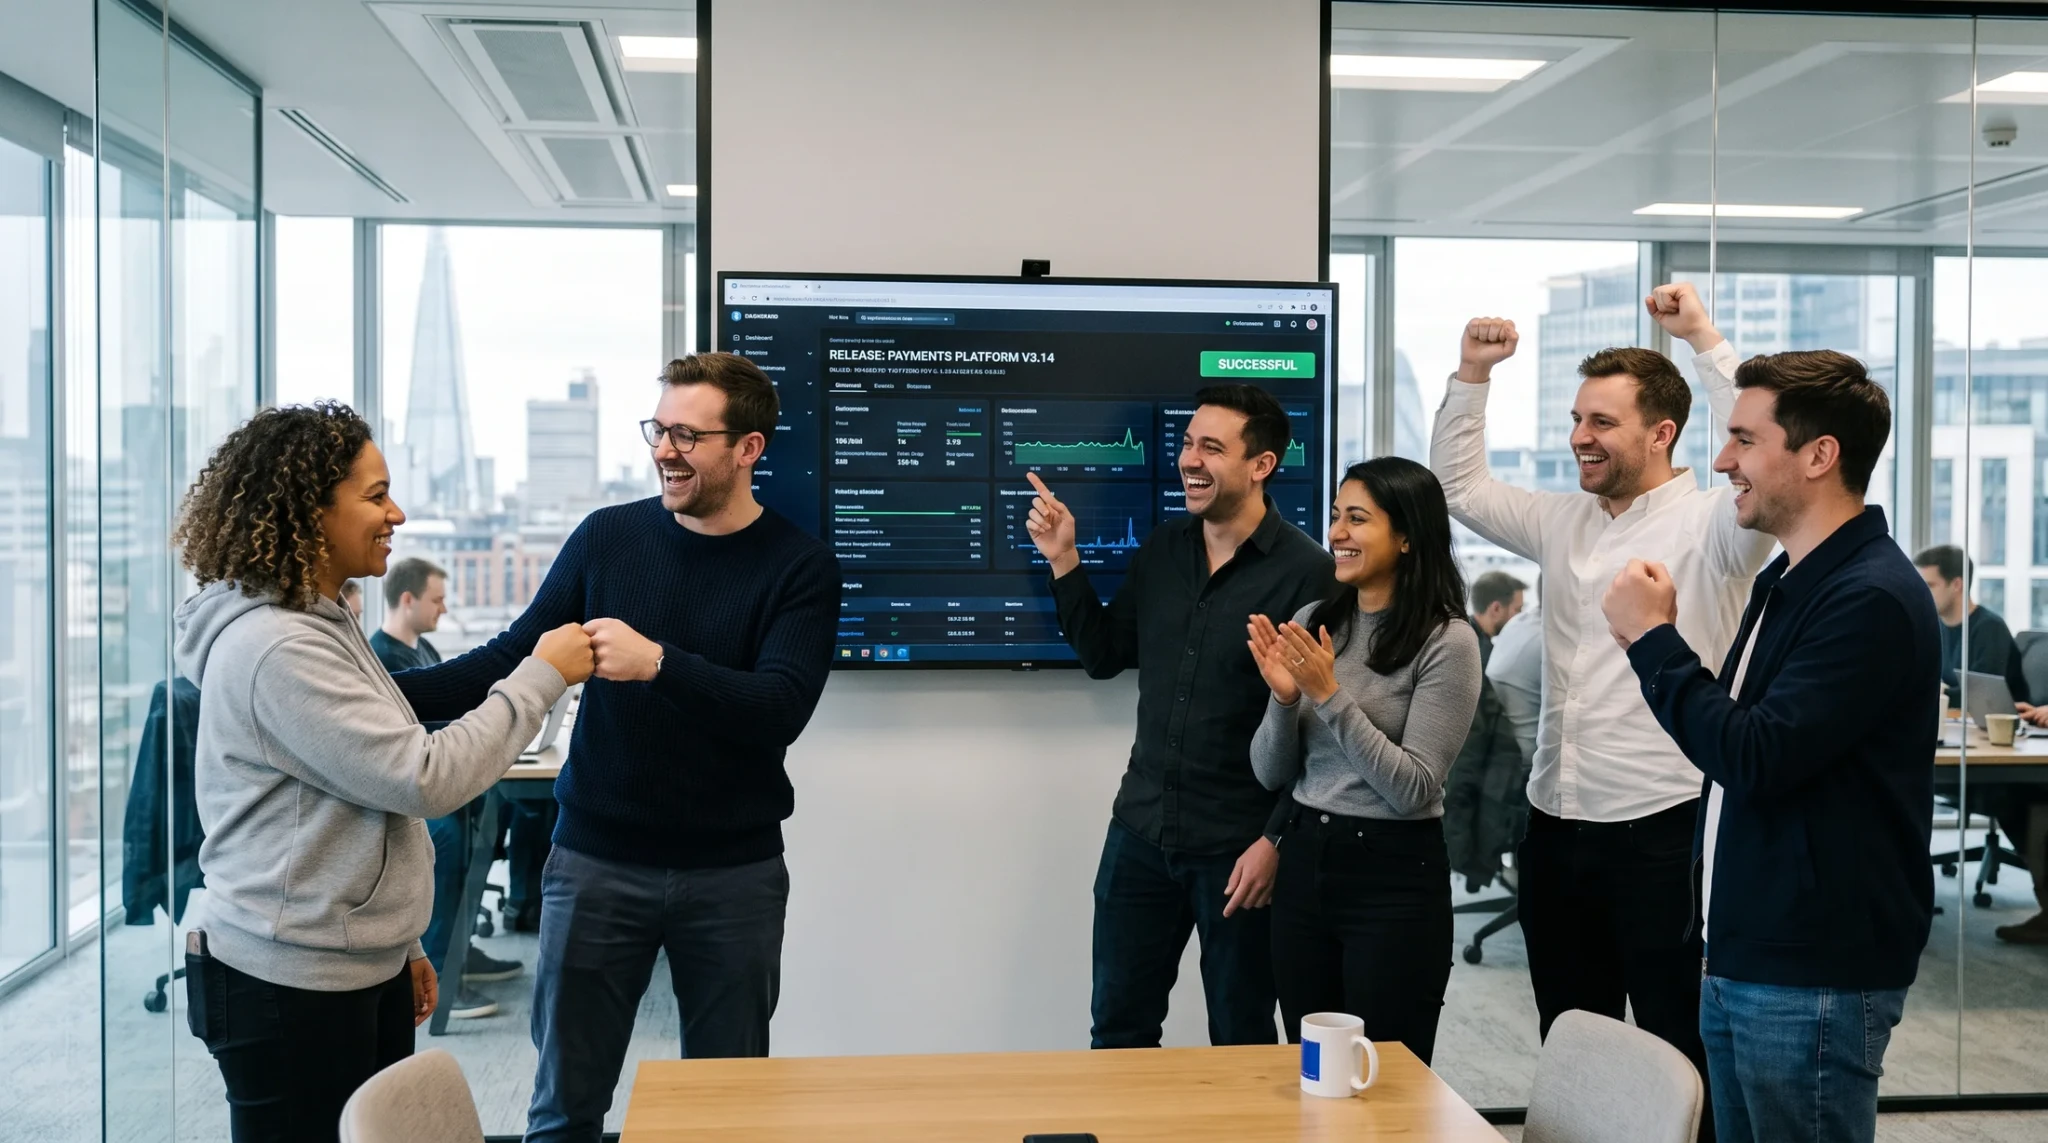
SOC 2 in eleven weeks, with a team of two.
Lumen PayTomás Reyes · CTO
- 11weeks to a clean SOC 2 Type II report
- 86controls mapped to live checks
- 4days of team time for the second audit
- 01
Challenge
Found openLumen Pay needed a SOC 2 Type II report to sign its first bank. The team had three engineers who could gather evidence, and all three were building the product.
- 02
Approach
In progressEach control was mapped once to live checks across identity, devices and cloud. Evidence was collected daily, and the auditor was given a read-only login.
- 86 controls mapped in the first week
- Failing checks became findings with owners
- No screenshots were taken
- 03
Result
SecuredThe report came back clean eleven weeks after kick-off, and the bank contract was signed the same month. The second audit took four days of the team's time.
Case 04 · Fintech · 210 seats
SOC 2 in eleven weeks, with a team of two.
Lumen PayTomás Reyes · CTO
- 11weeks to a clean SOC 2 Type II report
- 86controls mapped to live checks
- 4days of team time for the second audit
- 01
Challenge
Found openLumen Pay needed a SOC 2 Type II report to sign its first bank. The team had three engineers who could gather evidence, and all three were building the product.
- 02
Approach
In progressEach control was mapped once to live checks across identity, devices and cloud. Evidence was collected daily, and the auditor was given a read-only login.
- 86 controls mapped in the first week
- Failing checks became findings with owners
- No screenshots were taken
- 03
Result
SecuredThe report came back clean eleven weeks after kick-off, and the bank contract was signed the same month. The second audit took four days of the team's time.
What teams say
The first sweep usually pays for the year.
Security and IT leads on what turned up in week one, and what they stopped worrying about after.
01 of 05
Closed02
“It ranks by what an attacker would do next. My team stopped arguing about severity and started closing things.”
Closed03
“Our auditor logged in, read the evidence and left. No screenshots, no spreadsheet, no three-week scramble.”
Closed04
“A key hit a public repository at 2 am. Palisade had it revoked before I had found my glasses.”
Closed05
“Depot managers fix their own devices now, because the message tells them exactly what to press.”
What teams say
The first sweep usually pays for the year.
Security and IT leads on what turned up in week one, and what they stopped worrying about after.
01 of 05
Closed01
“The first sweep found a global admin who had left the company seven months earlier. That one finding paid for the year.”
Closed02
“It ranks by what an attacker would do next. My team stopped arguing about severity and started closing things.”
Closed03
“Our auditor logged in, read the evidence and left. No screenshots, no spreadsheet, no three-week scramble.”
Closed04
“A key hit a public repository at 2 am. Palisade had it revoked before I had found my glasses.”
Closed05
“Depot managers fix their own devices now, because the message tells them exactly what to press.”
Start here
Run the sweep on your domain.
Tell us where to look. We set up a read-only connection with you on a short call, and you see your own findings the same day.
We will sweep
- Identity providerNot connected
- Cloud accountsNot connected
- DevicesNot connected
- Code repositoriesNot connected
Start here
Run the sweep on your domain.
Tell us where to look. We set up a read-only connection with you on a short call, and you see your own findings the same day.
We will sweep
- Identity providerNot connected
- Cloud accountsNot connected
- DevicesNot connected
- Code repositoriesNot connected
Start here
Run the sweep on your domain.
Tell us where to look. We set up a read-only connection with you on a short call, and you see your own findings the same day.
We will sweep
- Identity providerNot connected
- Cloud accountsNot connected
- DevicesNot connected
- Code repositoriesNot connected